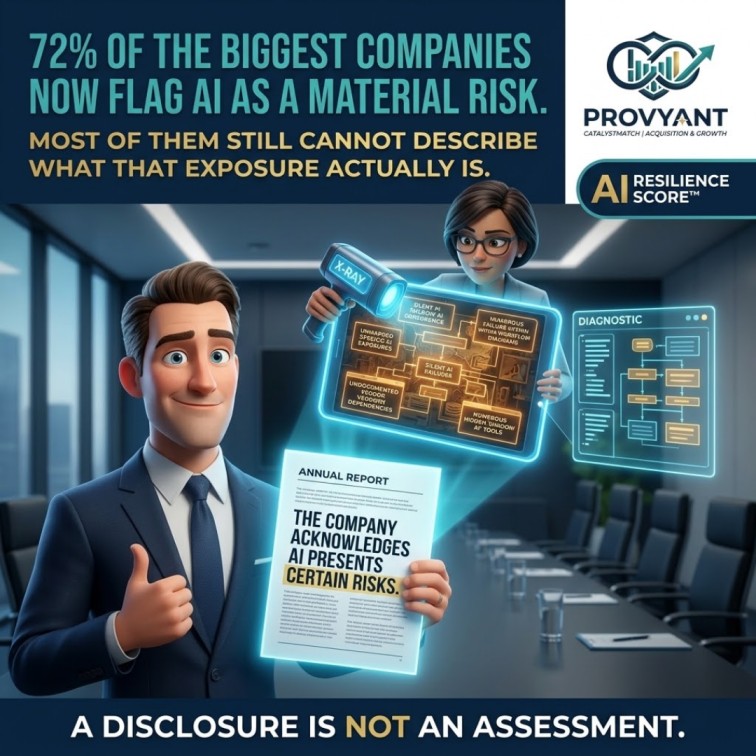
Every business documents the risks it understands. Market competition, supply chain disruption, key person dependency, regulatory change. These appear in planning documents, board reports, and, for public companies, formal disclosures. They are the known risks, the ones with established frameworks for measurement and management.
Then there is the risk that is now embedded in nearly every operation, growing quietly, and largely undocumented in any meaningful way. As Provyant has outlined in its analysis of why AI risk is now a line item on every business plan, artificial intelligence has become an operational dependency that most organisations have not yet learned to assess, let alone disclose with any real specificity. It is the operational risk hiding in plain sight.
The Risk That Went From Footnote to Front Page
The speed at which AI became a recognised material risk is one of the fastest shifts in the history of corporate risk disclosure.
72% of S&P 500 companies now flag AI as a material risk in their public disclosures, up from just 12% in 2023, according to The Conference Board and ESGAUGE. That is a sixfold increase in two years. 380 of the S&P 500 companies added or expanded descriptions of AI as a material risk in their 2025 annual filings, according to an Autonomy Institute report.
The largest technology companies have made the shift explicit. Alphabet, Amazon, Meta, and Netflix have fundamentally shifted their disclosures from innovation-led growth to material operational risk, highlighting the potential for model failure to disrupt core revenue streams. When the companies building the technology are reclassifying it from opportunity to operational risk, the signal for everyone else is unambiguous.
Why the Disclosure Is Real but the Understanding Is Not
Here is the uncomfortable part. The fact that a business acknowledges AI risk does not mean it understands its own exposure. And that gap is where the real danger sits.
Vague or generic descriptions of AI risks are a warning sign. If a company’s disclosure is boilerplate language that could apply to any business, the management team may not have thought through its actual exposures. The presence of an AI risk statement is not the same as a genuine assessment of where AI sits in critical operations, what happens when it fails, and who is accountable for the outcome.
This is the operational risk nobody actually puts in their annual report: not the generic acknowledgment that AI carries risk, but the specific, honest mapping of where the business is genuinely exposed. The complexity and limited transparency of many AI models, combined with the pace of technological change, may make it difficult for companies to fully understand AI system behaviour, identify risks, or anticipate unintended consequences. In other words, many businesses cannot describe their exposure precisely because they have not done the work to understand it.
What the Real Operational Exposure Looks Like
The operational risk that goes undocumented is specific and identifiable once a business actually looks for it.
Dependency risk. AI accelerates the speed and scale of operational failure and amplifies dependencies on third-party systems. When a business embeds a third-party AI tool into a critical workflow, it inherits the reliability, pricing, and availability risk of that vendor. Most businesses have not mapped these dependencies, which means they cannot answer the basic question of what happens operationally when a key AI system changes or fails.
Silent failure risk. Unlike a system outage, AI degradation does not always announce itself. Outputs drift. Decisions built on unreliable AI recommendations compound before anyone traces the source. This is the category of operational risk least likely to appear in any formal document precisely because it is the hardest to see until it has already caused damage.
Cybersecurity exposure. AI-crafted phishing emails show click-through rates of around 54%, compared with approximately 12% for traditional attacks, according to CrowdStrike’s 2025 analysis. AI has expanded the attack surface and armed adversaries with more sophisticated tools, and smaller organisations without enterprise security infrastructure are disproportionately exposed.
Shadow AI risk. The AI tools being used across an organisation without leadership visibility create exposure that by definition does not appear in any risk assessment, because leadership does not know it is happening. The SEC’s 2026 examination priorities reveal that AI has shifted from an emerging fintech area to a clear area of operational risk, linked to cybersecurity, disclosures, and internal use for critical functions.
Why This Matters Beyond Public Companies
The disclosure conversation is framed around public companies because they are legally required to file risk factors. But the underlying operational risk applies to every business, and it carries a particular consequence for private companies approaching a sale, a succession, or a capital raise.
A business that cannot articulate its AI exposure, that has not mapped where AI sits in its operations or what happens when it fails, is a business that a sophisticated buyer or lender cannot adequately underwrite. As Provyant has outlined in its analysis of why buyers look beyond revenue, the ability to demonstrate structured risk management, including AI risk, is increasingly a component of how businesses are valued. The private business owner who has never documented AI risk is not avoiding the risk. They are simply deferring the moment it becomes visible, usually to the least convenient point, in the middle of due diligence.
The Invisible Recession Provyant tracks is already surfacing in businesses that carried undocumented operational risk into a transition and discovered its cost only when a buyer or lender ran the numbers.
From Undocumented to Understood
The operational risk nobody puts in their annual report is not unmanageable. It is simply unexamined in most businesses. Closing that gap does not require sophisticated tooling. It requires an honest, structured assessment of where AI sits in the operation, what depends on it, what happens when it fails, and who is accountable.
That is precisely the work that turns an undocumented risk into a managed one. As Provyant has outlined in its analysis of operational continuity in the age of AI, the businesses that assess their AI exposure deliberately are the ones that hold their value and their operational stability through disruption.
The Risk You Name Is the Risk You Can Manage
The businesses that navigate AI disruption most effectively are not the ones with the most reassuring risk disclosures. They are the ones that did the uncomfortable work of understanding their actual exposure, naming it specifically, and building the structures to manage it before it surfaced on its own terms.
The AI Resilience Score at provyant.com gives business owners, buyers, and advisors the structured framework to assess AI operational risk across the dimensions that matter, the ones that rarely make it into any formal document until it is too late. Because the operational risk that goes unnamed is the one that decides the outcome when everyone else is still calling it an emerging technology.